
Audit Trail Integrity in Automated Reconciliation: Standards & Best Practices
Financial reconciliation has evolved from manual spreadsheet matching to complex, AI-driven autonomous operations. In this high-stakes environment, the integrity of the audit trail is not merely a compliance checkbox. It is the foundational bedrock of trust between financial institutions, family offices, and their operational partners. According to recent industry analyses on financial technology adoption, organizations leveraging automated reconciliation report a 40% reduction in close-cycle times, yet the complexity of data ingestion increases the risk of untraceable breaks. This guide explores the essential features and standards required to maintain absolute audit trail integrity in automated systems.
What is Audit Trail Integrity?
Before diving into technical specifications, it is crucial to define the core concept. Audit trail integrity is the assurance that every data point, decision, and transformation within a financial process is recorded, immutable, and traceable to its original source. In the context of automated reconciliation, this means that when an AI agent resolves a discrepancy, the system must provide a complete, unalterable history of how that resolution was reached.
Without this integrity, the automation itself becomes a liability. If a break in the ledger is resolved by an algorithm, but the reasoning is lost or the data source is ambiguous, the financial close cannot be audited. This leads to regulatory penalties, operational blind spots, and a loss of stakeholder confidence. The goal of modern reconciliation platforms is to ensure that every action is logged, every decision is explained, and the full reasoning trail is preserved for future review.
Core Features for Unbroken Chains
To achieve true audit trail integrity, an automated reconciliation system must possess specific architectural capabilities. These features ensure that the chain of custody for financial data remains unbroken from ingestion to final reporting.
1. Immutable Logging and Timestamping
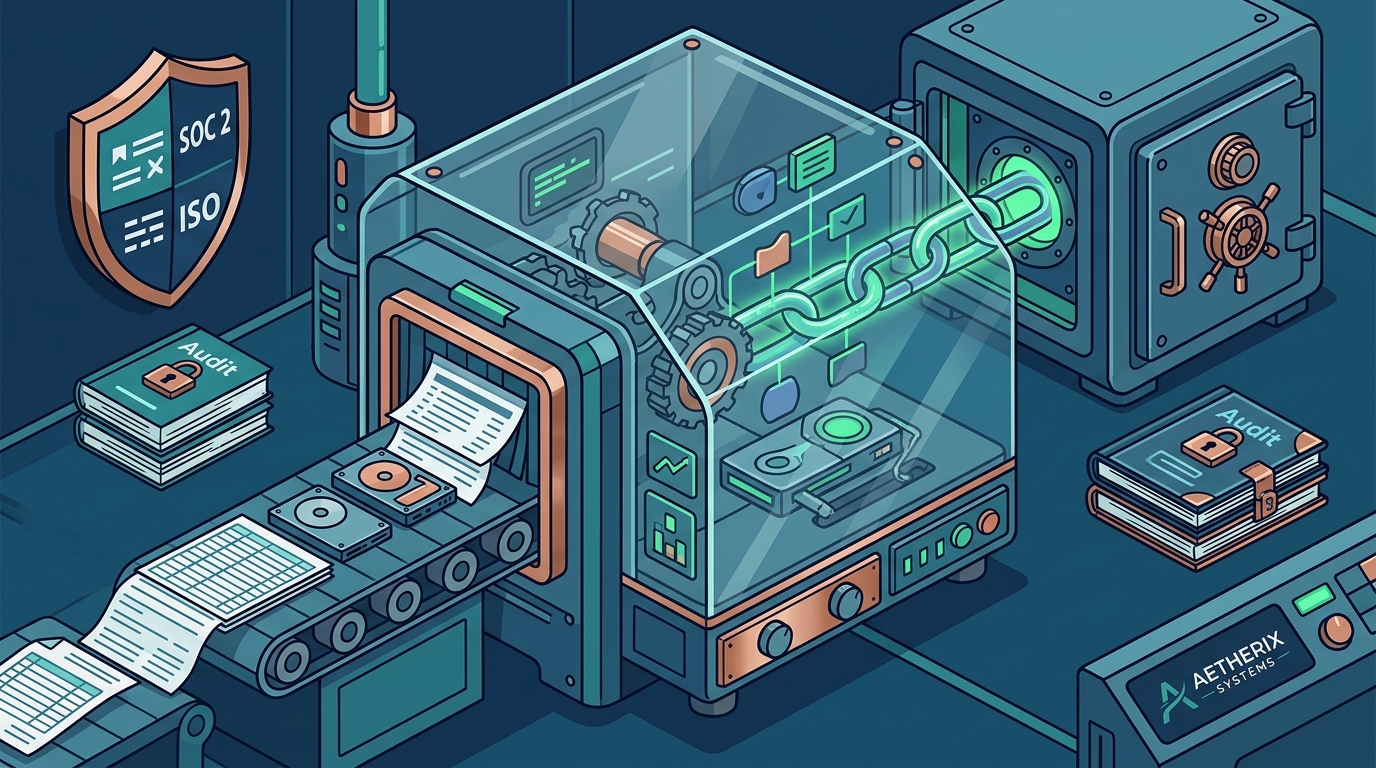
The foundation of any audit trail is the ability to record events in a way that prevents alteration. This requires immutable logging mechanisms where every data ingestion, matching attempt, and resolution proposal is stamped with a precise, synchronized timestamp. These logs must be stored in a write-once-read-many (WORM) format or similar secure storage architecture. This ensures that historical records cannot be retroactively modified, providing a reliable source of truth for auditors.
2. End-to-End Traceability
Traceability allows users to follow a transaction from its origin to its final state. In automated reconciliation, this means linking the final reconciled entry back to the original custodian statement, bank feed, or ledger entry. When an agent investigates a break, it must attach the full reasoning, including the documents reviewed and the logic applied. This creates a transparent narrative that explains not just what happened, but why it happened.
3. Role-Based Access Control (RBAC)
Integrity is compromised if unauthorized users can view or modify audit logs. Robust systems implement strict role-based access controls, ensuring that only designated compliance officers, auditors, and system administrators can access sensitive audit data. This minimizes the risk of internal fraud and ensures that the audit trail remains a secure, trusted record.
4. Automated Exception Handling with Context
Standard reconciliation tools often flag exceptions without context. Advanced systems, particularly those utilizing AI agents, must provide context-rich exception handling. When a break is identified, the system should automatically gather relevant data points, such as previous matching attempts, vendor details, and historical patterns, and present them to the agent or human reviewer. This contextual data becomes part of the audit trail, enriching the record of the resolution process.
Compliance Standards & Frameworks
Audit trail integrity is not just an operational best practice. It is a regulatory requirement. Financial institutions and service providers must adhere to strict global standards to ensure their data handling and reporting meet legal obligations.
SOC 2 Type II Compliance
The Service Organization Control 2 (SOC 2) Type II report is the gold standard for service providers handling sensitive data. It evaluates the effectiveness of security, availability, processing integrity, confidentiality, and privacy controls over a period of time. For reconciliation systems, processing integrity is paramount. The audit trail serves as the primary evidence for SOC 2 auditors, demonstrating that data is processed completely, accurately, and timely. Aetherix Systems maintains rigorous SOC 2 Type II compliance, ensuring that every reconciliation operation meets these stringent criteria.
GDPR and Data Residency
The General Data Protection Regulation (GDPR) in the European Union imposes strict rules on how personal data is processed and stored. While financial data is often anonymized, audit trails may contain metadata that falls under GDPR purview. Compliance requires that data processing activities are documented, and individuals have the right to access their data. Furthermore, data residency requirements dictate where this data can be stored. Aetherix Systems supports multiple data residency regions, allowing clients to ensure their audit trails and financial data remain within specific geographic boundaries, such as the EU or UAE.
ISO/IEC 27001 and 42001
ISO/IEC 27001 is the international standard for information security management systems (ISMS). It provides a framework for managing sensitive company information so that it remains secure. ISO/IEC 42001 is the first international standard for artificial intelligence management systems (AIMS). For AI-driven reconciliation, adherence to both standards is critical. It ensures that the AI agents operating the reconciliation are governed by the same rigorous security and ethical standards as the underlying data. Aetherix Systems is compliant with ISO/IEC 42001:2023, demonstrating its commitment to responsible AI governance.
UAE PDPL and Global Regulations
As financial operations become increasingly global, compliance with local regulations is essential. The UAE Personal Data Protection Law (PDPL) establishes comprehensive requirements for data processing within the United Arab Emirates. Similarly, other regions have their own data protection and financial reporting laws. A robust audit trail must be adaptable to these varying legal landscapes, ensuring that data handling practices align with local mandates.
Challenges in AI-Driven Reconciliation
While AI agents offer significant advantages in speed and accuracy, they introduce unique challenges for audit trail integrity. The "black box" nature of some AI models can make it difficult to understand how a specific decision was reached. This lack of transparency is unacceptable in financial reconciliation.
Explainability and Interpretability
To maintain integrity, AI agents must be explainable. This means that for every resolution proposed by an agent, the system must provide a clear, human-readable explanation of the logic used. This includes citing the specific data points, rules, or patterns that led to the decision. Without explainability, the audit trail is incomplete, and the reconciliation cannot be trusted.
Handling Edge Cases
AI agents are trained on historical data, but financial transactions often include unique edge cases. When an agent encounters a scenario it has not seen before, it must either flag it for human review or apply a conservative resolution strategy. The audit trail must clearly distinguish between automated resolutions and human-reviewed exceptions. This distinction is vital for auditors to assess the reliability of the automated process.
Data Ingestion Variability
Reconciliation involves ingesting data from multiple sources, including custodians, banks, and internal ledgers. Each source may have different formats, update frequencies, and error rates. The audit trail must capture the state of the data at the moment of ingestion, including any transformations or normalizations applied. This ensures that any discrepancies can be traced back to the source data, rather than the processing logic.
Implementation Strategy
Implementing a reconciliation system with robust audit trail integrity requires a strategic approach. It is not just about selecting the right technology. It is about aligning operational workflows with compliance requirements.
1. Define Audit Requirements Early
Before selecting a platform, organizations must define their specific audit requirements. This includes identifying the regulatory frameworks that apply, the types of data that need to be tracked, and the retention periods for audit logs. This clarity ensures that the chosen system can meet all necessary compliance standards from day one.
2. Choose a Platform with Native Audit Capabilities
Not all reconciliation platforms offer the same level of audit trail integrity. Look for systems that provide full visibility into every agent's operations, including tasks processed, decisions made, and outcomes delivered. Aetherix Systems provides real-time monitoring and comprehensive reporting, ensuring that every step of the reconciliation process is logged and explainable.
3. Integrate with Existing Tech Stack
Seamless integration with existing ERP systems, such as NetSuite, Sage Intacct, or Microsoft Dynamics, is crucial. The audit trail must span across these systems, linking data from the reconciliation platform to the general ledger. This end-to-end visibility ensures that financial reports are accurate and auditable.
4. Continuous Monitoring and Optimization
Audit trail integrity is not a one-time setup. It requires continuous monitoring to ensure that logs are being generated correctly and that no data is being lost. Regular audits of the audit trail itself can help identify gaps in coverage or potential security vulnerabilities. Aetherix Systems offers continuous monitoring and performance analytics to help clients optimize their reconciliation operations.
Key Takeaways
- Immutable Logging: Audit trails must be stored in a write-once-read-many format to prevent retroactive modification.
- Explainable AI: AI agents must provide clear, human-readable reasoning for every resolution to maintain trust.
- SOC 2 Compliance: Processing integrity is a core component of SOC 2 Type II, requiring rigorous audit trail documentation.
- Data Residency: Compliance with GDPR and UAE PDPL requires control over where audit data is stored.
- End-to-End Traceability: Every transaction must be traceable from its source to its final reconciled state.
- Role-Based Access: Strict access controls are necessary to protect the integrity of the audit trail from internal threats.
- Continuous Monitoring: Regular audits of the audit trail itself are essential for maintaining long-term compliance.
Frequently Asked Questions
What is the primary purpose of an audit trail in reconciliation?
The primary purpose is to provide a complete, unalterable record of all financial transactions and decisions, ensuring accountability and compliance with regulatory standards.
How do AI agents impact audit trail integrity?
AI agents can enhance integrity by providing consistent, data-driven resolutions, but they must be explainable to ensure that their decisions can be audited and understood by humans.
Is SOC 2 compliance required for reconciliation software?
While not always legally mandated, SOC 2 Type II compliance is an industry standard that demonstrates a provider's commitment to security and processing integrity, which is critical for financial data.
What is the difference between SOC 2 Type I and Type II?
SOC 2 Type I evaluates the design of controls at a specific point in time, while Type II evaluates the operational effectiveness of those controls over a period of time, typically six to twelve months.
How does data residency affect audit trails?
Data residency requirements dictate where data can be stored geographically. Audit trails must be stored in compliance with these regulations to avoid legal penalties and ensure data sovereignty.
Can audit trails be modified after creation?
No, a core principle of audit trail integrity is immutability. Once a log entry is created, it should not be alterable to preserve its reliability as a source of truth.
What are the key benefits of automated reconciliation?
Automated reconciliation reduces close-cycle times, minimizes human error, and provides real-time visibility into financial data, leading to more accurate and timely financial reporting.
How does Aetherix Systems ensure compliance?
Aetherix Systems maintains compliance with multiple global frameworks, including SOC 2, GDPR, and ISO/IEC 42001, through rigorous security practices, data residency options, and continuous monitoring.
Secure Your Reconciliation Operations
In an era of increasing regulatory scrutiny and operational complexity, the integrity of your audit trail is your most valuable asset. Do not leave your financial close to chance. Partner with a provider that understands the nuances of enterprise autonomy and compliance. Book a scoping call with Aetherix Systems today to learn how our AI agents can deliver clean, auditable results for your organization.