
What Should a Fund Administrator Verify in a Reconciliation Audit Trail?
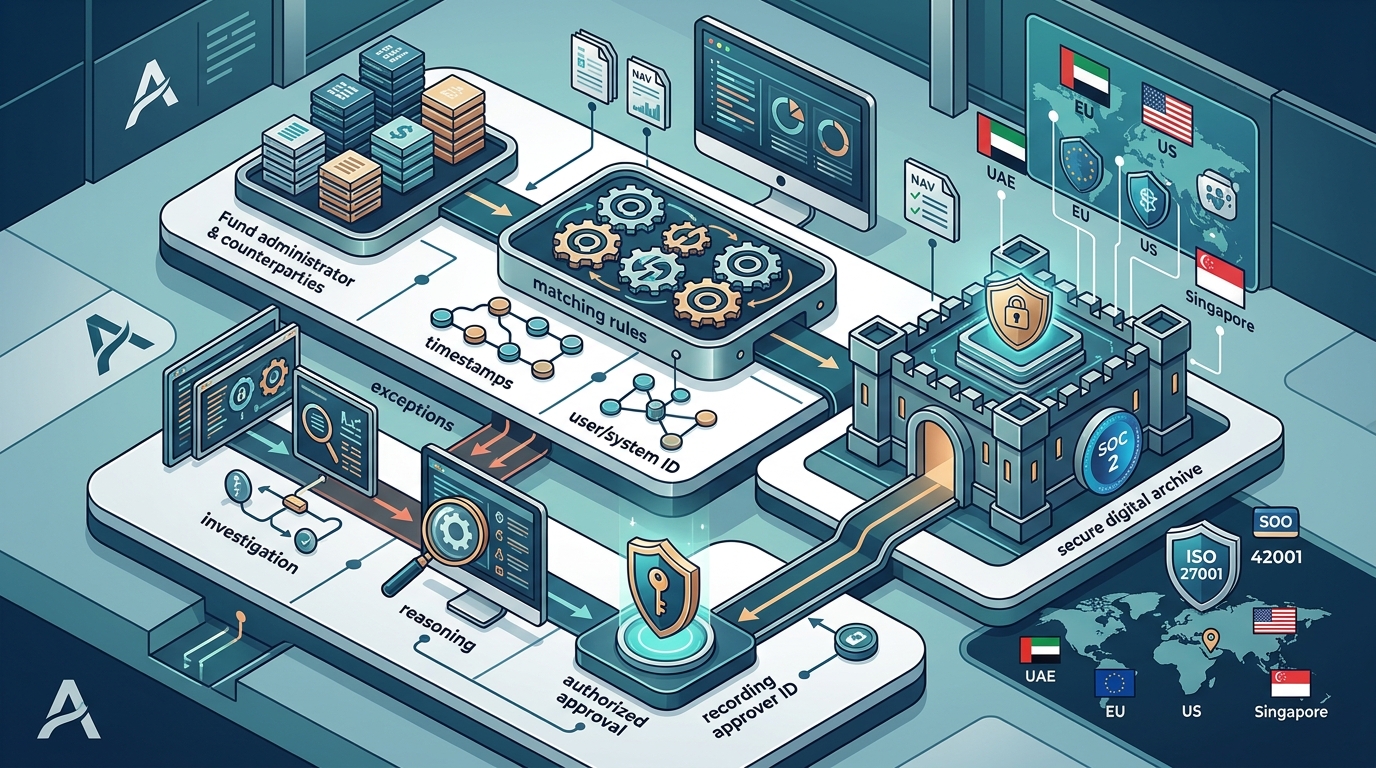
A fund administrator should verify that every reconciliation action is timestamped, attributed to a specific user or system, and supported by source documentation. The audit trail must prove that matching rules were applied consistently, exceptions were investigated with reasoning, and resolutions were approved by authorized personnel. This guide covers the specific data points, workflow controls, and compliance standards required to maintain a defensible audit trail in 2026.
How to Choose: Separating Good from Bad
Choosing a reconciliation platform or service requires distinguishing between simple matching engines and systems that provide true investigative depth. A basic matching engine flags discrepancies but leaves the investigation to human analysts. A robust audit trail requires a system that documents the reasoning behind every decision. When evaluating options, look for systems that capture the full context of an exception, including the source documents pulled, the logic applied, and the final resolution proposed.
Depth of Reasoning
The primary differentiator is the depth of the reasoning trace. A good system does not just say "mismatch found." It explains why the mismatch occurred, such as a timing difference or a data entry error. It attaches the relevant source documents, like bank statements or custodian reports, to the exception record. This level of detail is critical for audit defense. If a system only provides a binary match or no-match status, it fails to provide the evidence needed for a comprehensive audit.
Immutability and Access Control
Another critical factor is the immutability of the log. Once an action is recorded, it should not be editable or deletable. Access controls must ensure that only authorized personnel can view or approve specific actions. Role-based access control (RBAC) is essential to prevent unauthorized changes to the audit trail. The system should also support multi-factor authentication for all users interacting with the reconciliation process.
What to Ask: Pre-Commitment Questions
Before committing to a reconciliation provider, ask specific questions about their data handling and audit capabilities. These questions help verify that the provider can meet your compliance requirements and operational needs.
Data Retention and Export
Ask how long audit logs are retained and in what format. Can you export the full audit trail in a machine-readable format, such as JSON or CSV? This is crucial for integrating with your own compliance systems or for providing data to external auditors. Ensure that the provider offers a clear data retention policy that aligns with your regulatory obligations.
Integration Capabilities
Inquire about the provider's integration capabilities with your existing systems. Can they connect to your ERP, custodian portals, and bank feeds via APIs? Do they support webhook-driven architectures that allow real-time updates? A provider that requires manual file uploads may introduce delays and increase the risk of data entry errors, which can compromise the integrity of the audit trail.
How to Verify: Checking Credentials
Verifying a provider's credentials involves checking their compliance with recognized security and AI governance standards. Look for evidence of compliance with frameworks such as SOC 2 Type II, ISO/IEC 27001, and ISO/IEC 42001. These standards ensure that the provider has implemented robust security measures and AI governance practices.
Security Standards
Check for SOC 2 Type II compliance, which provides assurance about the provider's security, availability, processing integrity, confidentiality, and privacy. Also verify ISO/IEC 27001 compliance, which focuses on information security management. These certifications indicate that the provider has undergone independent audits and maintains high standards of security.
AI Governance
For AI-driven reconciliation systems, verify compliance with ISO/IEC 42001, the international standard for AI management systems. This standard ensures that the provider has established processes for managing the risks associated with AI systems, including bias, transparency, and accountability. It is a critical credential for any provider using AI agents in financial operations.
How It Works: Workflow and Sequence
Understanding the workflow of a reconciliation system helps you verify that the audit trail captures every step of the process. A typical workflow involves four stages: ingestion, matching, investigation, and reporting. Each stage generates specific data points that contribute to the audit trail.
Ingestion and Normalization
The process begins with ingesting data from various sources, such as banks, custodians, and internal ledgers. The system normalizes this data, ensuring that formats, currencies, and identifiers are consistent. The audit trail records the source of each data point, the timestamp of ingestion, and any transformations applied during normalization.
Matching and Exception Handling
Next, the system applies matching rules to compare records. When a mismatch is detected, the system flags it as an exception. The audit trail records the matching rules applied, the specific fields that did not match, and the tolerance thresholds used. For each exception, the system initiates an investigation, pulling supporting documents and analyzing the root cause. The reasoning behind the proposed resolution is documented in the audit trail.
What It Costs: Price Drivers
The cost of reconciliation services or software depends on several factors, including the volume of transactions, the complexity of the data, and the level of automation required. Understanding these drivers helps you budget accurately and avoid unexpected costs.
Transaction Volume
Most providers charge based on the number of transactions processed. Higher volumes typically result in lower per-transaction costs due to economies of scale. However, complex transactions, such as those involving multiple currencies or derivatives, may incur higher fees. It is important to clarify the pricing model with your provider to ensure it aligns with your operational needs.
Customization and Integration
Customization and integration costs can significantly impact the total price. If you require custom matching rules, specific integrations with legacy systems, or tailored reporting, these features may come at an additional cost. Evaluate the level of customization you need and factor it into your budget. A provider that offers a flexible pricing model, such as pay-for-outcomes rather than software seats, may be more cost-effective for your organization.
What Goes Wrong: Common Mistakes
Common mistakes in reconciliation audit trails include incomplete documentation, lack of immutability, and insufficient access controls. These mistakes can undermine the integrity of the audit trail and expose your organization to regulatory risk.
Incomplete Documentation
One of the most common mistakes is failing to document the reasoning behind every decision. If the audit trail only records the final outcome without the supporting evidence, it is insufficient for audit defense. Ensure that your system captures the full context of each action, including the source documents, the logic applied, and the approval workflow.
Lack of Immutability
Another critical mistake is allowing edits or deletions to the audit log. Once an action is recorded, it should be immutable. If users can modify or delete entries, the integrity of the audit trail is compromised. Verify that your system enforces immutability and provides a clear history of any changes made to the configuration or rules.
Versus Alternatives: Comparison
Comparing AI-driven reconciliation systems with traditional rules-based engines highlights the advantages of agentic workflows. Rules-based engines are effective for straightforward matching but lack the ability to investigate complex exceptions. AI-driven systems, on the other hand, can analyze the context of an exception and propose a resolution with full reasoning.
| Feature | Rules-Based Engine | AI-Driven System |
|---|---|---|
| Matching Capability | High for exact matches | High for exact and fuzzy matches |
| Exception Investigation | Manual | Automated with reasoning |
| Audit Trail Depth | Basic (match/no-match) | Comprehensive (reasoning, docs) |
| Scalability | Limited by human capacity | High, parallel processing |
For a Specific Situation: Multi-Custodian Funds
For fund administrators managing multi-custodian funds, the audit trail must account for the complexity of reconciling positions across multiple custodians. Each custodian may use different data formats, naming conventions, and reporting schedules. The system must normalize this data and provide a clear audit trail that links each position to its source custodian.
Source Ownership and Cutoff
In multi-custodian environments, source ownership and cutoff are critical. The audit trail must clearly indicate which custodian is the authoritative source for each field and event. It should also record the cutoff time for each data feed, ensuring that all records are included in the correct reporting period. This level of detail is essential for resolving discrepancies and maintaining accurate books.
Rules and Protections: Regulatory Standards
Regulatory standards require fund administrators to maintain robust audit trails that demonstrate compliance with accounting and financial reporting standards. These standards include IFRS 10 and ASC 810, which govern the consolidation of financial statements. The audit trail must provide evidence that intercompany transactions are eliminated correctly and that all balances are accurate.
Data Protection
Data protection regulations, such as GDPR and UAE PDPL, require that personal data is processed lawfully and securely. The audit trail must include records of data processing activities, including the lawful basis for processing, data protection impact assessments, and data subject rights requests. Compliance with these regulations is essential for maintaining trust with clients and regulators.
Local Specifics: GCC and Global Operations
For fund administrators operating in the GCC, local data residency requirements are a critical consideration. The UAE Personal Data Protection Law (PDPL) requires that personal data is stored and processed within the UAE, unless specific safeguards are in place. Aetherix Systems, based in Dubai, offers data residency options in the UAE, EU, and US, ensuring compliance with local regulations.
Multi-Jurisdictional Compliance
Operating across multiple jurisdictions requires a multi-jurisdictional compliance approach. The audit trail must reflect the specific regulatory requirements of each jurisdiction, including data residency, privacy, and AI governance. Aetherix Systems maintains compliance with global data protection regulations and AI governance frameworks, providing a robust audit trail that meets the needs of multi-jurisdictional operations.
Timing: When to Act
Timing is critical in reconciliation. Delays in resolving exceptions can lead to compounding errors and regulatory penalties. A robust audit trail helps you identify and resolve exceptions quickly, reducing the risk of errors and improving the speed of your close process. By automating the investigation and resolution of exceptions, you can compress your close cycle and deliver clean reconciliations on your schedule.
Results Over Time: Long-Term Outcomes
Over time, a robust audit trail provides measurable outcomes, including reduced close times, improved accuracy, and enhanced compliance. By continuously monitoring and optimizing the reconciliation process, you can identify trends, detect anomalies, and improve the efficiency of your operations. The audit trail serves as a valuable asset for continuous improvement, providing insights into the performance of your reconciliation process and the effectiveness of your controls.
Key Takeaways
- Verify that the audit trail captures the full context of every action, including source documents and reasoning.
- Ensure the audit log is immutable and protected by role-based access control.
- Check for compliance with SOC 2 Type II, ISO/IEC 27001, and ISO/IEC 42001 standards.
- Understand the pricing model and factor in customization and integration costs.
- Avoid common mistakes such as incomplete documentation and lack of immutability.
- For multi-custodian funds, ensure the audit trail accounts for source ownership and cutoff.
- Comply with local data residency and privacy regulations, such as UAE PDPL and GDPR.
- Use the audit trail for continuous improvement and long-term operational efficiency.
Frequently Asked Questions
What is a reconciliation audit trail?
A reconciliation audit trail is a comprehensive log of all actions taken during the reconciliation process, including matching, investigation, and resolution. It provides evidence that the process was conducted accurately and in compliance with regulatory standards.
Why is an audit trail important for fund administrators?
An audit trail is important for fund administrators because it provides evidence of compliance with accounting and financial reporting standards. It helps defend against regulatory inquiries and ensures that the books are accurate and reliable.
What data points should be included in the audit trail?
The audit trail should include timestamps, user attribution, source documents, matching rules applied, exception details, reasoning for resolutions, and approval workflows. These data points provide a complete picture of the reconciliation process.
How does AI improve the audit trail?
AI improves the audit trail by automating the investigation of exceptions and documenting the reasoning behind every decision. This provides a deeper level of detail than traditional rules-based engines, which only record match or no-match statuses.
What are the regulatory requirements for audit trails?
Regulatory requirements for audit trails include compliance with accounting standards such as IFRS 10 and ASC 810, as well as data protection regulations like GDPR and UAE PDPL. The audit trail must demonstrate that the reconciliation process was conducted accurately and in compliance with these standards.
How can I verify a provider's compliance with security standards?
You can verify a provider's compliance by checking for certifications such as SOC 2 Type II, ISO/IEC 27001, and ISO/IEC 42001. These certifications indicate that the provider has undergone independent audits and maintains high standards of security and AI governance.
Conclusion
A robust reconciliation audit trail is essential for fund administrators to maintain compliance and ensure the accuracy of their books. By verifying that every action is timestamped, attributed, and supported by source documentation, you can defend against regulatory inquiries and improve the efficiency of your operations. Aetherix Systems provides AI-driven reconciliation services with a full audit trail on every action, helping you achieve a clean close with confidence. To learn more about how our agents can support your reconciliation process, .